

XRPL NFT Scam Tracker
The XRP-API.com NFT phishing-drain campaign tricks Xaman and other wallet users into signing "Safe XRPL verify message" transactions that drain their funds. This page tracks every confirmed drain on-chain and auto-updates as new scams are detected.
Campaign first observed 2023-07-31 · latest drain 2026-09-26 · data refreshed 0s ago
Ecosystem warning
David "JoelKatz" Schwartz, CTO of Ripple, has publicly warned XRPL users about this campaign. View on X →
Victim testimony
@xZBLUEx, FuzzyBear community member, was drained after accepting a bait NFT offer that swept his FUZZY holdings. View on X →
Fully understand any transaction before you sign it. Transactions on the XRP Ledger are final and cannot be reversed.
How victims are lured in
The hook. The attacker first social-engineers the victim with a fake airdrop, reward, staking, or token-claim opportunity, usually framed with urgency ("limited slots", "ends in 1 hour", "verify in the next 10 minutes"). The lure links to a phishing page that prompts you to connect your wallet. Connecting alone does not drain anything: the wallet just shares its address so the attacker can scan your balances. The drain only happens once you sign a transaction the attacker pushes to your wallet.
The same operator group runs multiple acquisition funnels in parallel:
- X / Twitter spam. Dozens of fake accounts posing as Xaman support, Xaman developers, or admins of trending projects. Profiles are padded with purchased followers and bot engagement (likes, replies, retweets) to look legitimate at a glance. They reply to real users in trending XRPL threads with "verification" instructions linking to the bait.
- Targeted impersonation. The dominant lure is Xaman("your wallet needs verification"), including fake events such as"Xaman Community Day" (no such event exists). Variants impersonate community-favorite projects like PHNIX, FuzzyBear, and other meme or DeFi tokens currently in the spotlight. The same drain mechanic adapts to whichever brand the victim trusts.
- Telegram & Discord DMs. After a user posts a support question or joins a project channel, attackers DM them within minutes claiming to be a "support agent" or "moderator". Attackers will also pose as fellow community members, striking up casual conversation to build rapport before pivoting to social engineering. They funnel the conversation off the official server and into a one-on-one DM where they push the verification link or terminal-paste command.
- "Exclusive group" bait. Inside a project's own Telegram or Discord, the target is invited to a privileged sub-group — a "whale group", an "OG holders" room, or a private alpha channel. Entry is gated behind a "membership verification": only after they agree to join are they asked to verify with their wallet — the same sign-to-drain trap. The exclusivity lowers the victim's guard because the invitation comes from inside a community they already trust.
- Google search hijacking. The campaign runs typo-squatted domains and pays for Google Ads slots that appear above the real result when users search for XRPL wallets, marketplaces, or token names. A single character difference in the URL bar (or just clicking the top "Sponsored" result) lands them on a clone site that runs the same scripts.
Common thread: the attacker's only goal is to get the victim onto a page they control, or to get them to sign a transaction or paste a terminal command without reading it. The on-chain drain or the malware payload then follows automatically.
Attack flow at a glance
End-to-end path from first contact to drained wallet:
Fake airdrop or reward on X, Discord, Telegram, or a Google-Ads phishing site.
Victim connects Xaman / Crossmark / GemWallet. Address shared, no funds moved yet.
Attacker pushes NFTokenCreateOffer prompts non-stop, disguised as 'verification'.
How the scam works (on-chain drain)
The attacker pre-targets the victim. After scanning their wallet, the attacker mints one NFT per asset the victim holds: XRP, LP tokens, IOUs, everything. Each NFT's URI encodes that specific balance, e.g. https://xrpl-api.com/api/nft/metadata?amount=11432359&asset=CSC%3ArCSCManTZ8ME…. The phishing endpoint dynamically returns matching metadata so each NFT renders in the victim's wallet as a stand-in for that exact balance, often dressed up to impersonate Xaman, XRPL.org, or a known marketplace.
The attacker then creates NFTokenCreateOffers with memos like "Verification: Safe XRPL verify message" plus "Info: idx:0;len:11". The wallet UI shows what looks like a routine verification, but each signature actually authorizes a sale of the targeted balance. Signing N "verifications" hands the attacker N specific assets: XRP first, then every held token.
When the victim signs, they are handing their XRP and tokens directly to the attacker. On-chain, the scammer has simply sold them an NFT. The attacker accepts the offer, the transfer settles as a normal on-chain payment indistinguishable from a legitimate trade, and the victim is left holding a worthless bait NFT. There is no path to reverse it.
How the attack got here. The earliest version of this campaign was crude: the attacker simply spammed NFTokenCreateOffer transactions at every wallet on the ledger, hoping a few victims would tap "accept" on whatever showed up in their inbox. Once wallets started flagging unsolicited offers as spam and hiding them by default, the operator shifted up the stack. The current variant abuses the wallet sign-in / push-notification flow: instead of pushing offers directly, the attacker lures the victim to a web app they control, where the page triggers a "verification" sign request that the wallet renders as a routine notification. The malicious payload is now wrapped in a UX the victim already trusts.
Evolving evasion. As detection has tightened across XRPL platforms and wallets, the campaign has shifted. The most recent variants mint blankNFTs with minimal or no on-chain metadata (no URI, no memo, sometimes no name), so URI and memo classifiers have nothing to match. We catch these by issuer-level reputation: any wallet that has ever produced a confirmed scam is auto-flagged on every subsequent mint and offer, URI or not. The list refreshes live and is published as scamIssuersList in the /api/nft/scam response so wallets can mirror it client-side.
Off-chain variant: terminal stealer payload
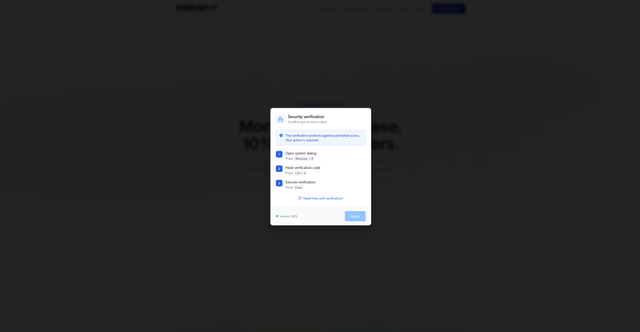
The same operators run a parallel attack that never touches the ledger. The bait NFT or a linked page prompts the user to "complete verification" by copying a string and pasting it into their desktop terminal (PowerShell on Windows, Terminal on macOS). The pasted line fetches a payload from a short-lived host (e.g. mmzzxcca.xyz/update3.zip) which deploys HijackLoaderplus SnappyClient, a commodity-stealer combo that exfiltrates browser cookies, saved passwords, and cryptocurrency wallet files, and installs persistence via a Run key plus DLL injection into SysWOW64\input.dll. See the public sandbox detonation at tria.ge/260505-k76d4afx2j (severity 10/10).
There is no XRPL signature involved: the loss happens entirely on the victim's machine, and the attacker can sweep funds from any wallet whose seed or session cookie was stored locally. Never paste anything from an NFT, Discord, Twitter, or website prompt into a terminal. No legitimate XRPL service ever asks you to do this.
Monthly drain timeline
| Month | XRP drained | Events |
|---|---|---|
| 2026-09 | 180.8K | 95 |
| 2026-08 | 421.4K | 130 |
| 2026-07 | 174.5K | 117 |
| 2026-06 | 173.5K | 132 |
| 2026-05 | 1.04M | 499 |
| 2026-04 | 227.3K | 135 |
| 2026-03 | 84.7K | 47 |
| 2026-02 | 394.9K | 164 |
| 2026-01 | 37.5K | 50 |
| 2024-11 | 15.5K | 11 |
| 2023-07 | 1 | 1 |
Top scammer wallets (XRP received)
| Address | XRP received | Drains |
|---|---|---|
| r3qAzD…x6ia | 576.5K | 10 |
| rKWQGG…MaTp | 304.3K | 101 |
| rG8Vfi…1UTq | 189.3K | 104 |
| rNszN3…eVq8 | 163.5K | 1 |
| rMKAzY…smaV | 155.9K | 39 |
| rJdgNk…sZ3A | 95.8K | 9 |
| rNZz8s…fNfP | 85.0K | 1 |
| rNRvAX…ev4k | 63.7K | 25 |
| rTgWnj…RgCk | 63.2K | 1 |
| rn98Kz…WRWu | 60.2K | 73 |
Top victim wallets (XRP paid)
| Address | XRP paid | Drains |
|---|---|---|
| rGhwR5…X2xG | 556.1K | 1 |
| rn6jfs…RvFB | 255.2K | 3 |
| rMubvu…Mpq5 | 163.5K | 1 |
| rhQ24R…WzD8 | 100.0K | 2 |
| rMvExi…79g3 | 94.3K | 1 |
| rQptSQ…E2BY | 85.0K | 1 |
| rnw9bP…T8ZT | 79.0K | 1 |
| rwqGza…iVyo | 63.2K | 1 |
| rLwT22…hZA4 | 51.5K | 1 |
| rw4vu6…Sm69 | 50.9K | 1 |
Scammer wallet holdings (live)
Current on-chain holdings of every scam wallet, XRP plus IOU/LP tokens at market value. Compare against the 2.75M XRP-equiv drained from victims: 100% has already been moved off-chain (cashed out, bridged, or pushed through a tumbler).
| Wallet | Total (XRP-eq) | Composition |
|---|---|---|
| rKWQGG…MaTp 6.17M REITF120.07M LP XRP/PONGO109.5K DARKNET497.1K RIBBLE | 1.1K | 41/1.0K XRP / Tokens |
| rMWj9F…RHAJ 1.63B DeepTide | 559 | 3/556 XRP / Tokens |
| rNt3n1…K8f1 | 191 | 191/0 XRP / Tokens |
| rfotNC…uPKU 56.30M $BWTZ0 RLUSD | 175 | 1/174 XRP / Tokens |
| rnsMwz…NcTD 11.11M ATM1.04M FUZZY0 MAG0 RLUSD | 111 | 7/104 XRP / Tokens |
| rNQyxw…pZ7y 1.7K RIPTARD | 91 | 91/0 XRP / Tokens |
| rMK9rP…iHCt | 75 | 75/0 XRP / Tokens |
| rMZGH5…JAtc 7 DROP892.5K XMEME6.37M SEAL1.31B PONGO | 73 | 55/18 XRP / Tokens |
| rHAbNx…jhog 50.0K FUZZY | 72 | 70/1 XRP / Tokens |
| rGtC5i…Z22M 35 RLUSD10.0K LP XRP9/XRP70.6K CSC728 LP Recieving: + 3 XRP/XRP | 69 | 20/50 XRP / Tokens |
| rJFiRE…bVj9 10.3K SOLO | 60 | 2/58 XRP / Tokens |
| ra9dRJ…8181 | 51 | 51/0 XRP / Tokens |
| r3wQ25…oNjq | 50 | 50/0 XRP / Tokens |
| roYZAe…6KXj | 43 | 43/0 XRP / Tokens |
| r38ypQ…tSNy 13.0K BEAR1.2K SOLO178.8K MXI306 XRT | 41 | 7/34 XRP / Tokens |
| rhT1f6…7CgZ 10.9K XPM | 36 | 1/35 XRP / Tokens |
| rhZExH…b1GV 46 RLUSD | 32 | 2/30 XRP / Tokens |
| rhLihS…Ys9F | 20 | 20/0 XRP / Tokens |
| rNvkAv…LH3Q 3.3K SOLO | 20 | 1/19 XRP / Tokens |
| rphrC8…MLP8 284.20M FIN463.7K editions14 BEAR6 RPR | 20 | 18/2 XRP / Tokens |
Snapshot from the last cron run (11s ago). Top 20 wallets shown. XRP cash Tokens LP chip
Potential dump pressure: tokens held by scammers
Aggregate token positions across all 2.4K tracked scam wallets. If any of these tokens see a large market sell, the scammers are likely behind it. Sorted by current XRP-equivalent.
| Token | Issuer | Amount held | Value (XRP) | Wallets |
|---|---|---|---|---|
| REITF | rLSCBS…LygX | 6.17M | 955 | 1 |
| DeepTide | rnHDzE…hbFi | 1.63B | 556 | 1 |
| $BWTZ | rrpQUE…GMHS | 56.30M | 174 | 1 |
| SOLO | rsoLo2…rLZz | 16.0K | 90 | 12 |
| RLUSD | rMxCKb…m5De | 107 | 71 | 193 |
| ATM | raDZ4t…23NZ | 11.11M | 61 | 3 |
| FUZZY | rhCAT4…pR62 | 1.56M | 46 | 77 |
| XPM | rXPMxB…wkoa | 11.5K | 37 | 13 |
| FLR | rcxJwV…o1Eu | 5.1K | 24 | 7 |
| BEAR | rBEARG…EqFW | 13.4K | 23 | 10 |
Top 10 of 40 distinct tokens, by current XRP-equivalent.
Tokens drained (top 40 by frequency)
Value in XRP uses current market price for regular tokens, or AMM pool reserves for LP tokens. - means no price feed (illiquid or delisted).
| RLUSD | rMxCKb…m5De | 3.9K | 2.6K | 43 |
| FUZZY | rhCAT4…pR62 | 714.78M | 20.7K | 40 |
| PHNIX | rDFXbW…ivmN | 2.15B | 14.5K | 27 |
| SOLO | rsoLo2…rLZz | 89.5K | 504 | 25 |
| REAL | rKVyXn…Nz88 | 285.1K | 217 | 17 |
| CSC | rCSCMa…gkwr | 436.17M | 15.8K | 17 |
| BXE | rM1J2M…y87r | 166.6K | 233 | 15 |
| 03C3BE9D…LP XRP/MAG | rNZ2ZV…bXce | 285.2K | 11.1K | 14 |
| VGB | rhcyBr…knaU | 38.3K | 172 | 13 |
| ARMY | rGG3wQ…CBfC | 117.4K | 669 | 11 |
Recent drains (live feed)
Every drain rebuilt as a three-step timeline: Minted — the attacker creates the bait NFT · Flagged — our detection marks it a scam · Drained — the victim signs the offer in their wallet. The gap between Flagged and Drained is our protection window: green when we flagged it in time, red when the signature beat us. Hover any address or hash for the full value.
| When | Paid | Mint → Flag → Drain | Victim → Scammer | On-chain |
|---|---|---|---|---|
5h ago Sep 26, 20:52:30 UTC | 14 XRP | Minted17:32:32+15d 3hFlagged20:52:24+6sDrained20:52:30 Flagged 6s before drain | rEM4Hr…MVD2 | NFT 000813… ↗tx 267A87… ↗ |
10h ago Sep 26, 16:36:41 UTC | 130 XRP | Minted01:16:00+21d 15hFlagged16:36:36+5sDrained16:36:41 Flagged 5s before drain | rhhNLW…x5tS | NFT 000813… ↗tx 1D0813… ↗ |
1d ago Sep 25, 21:46:50 UTC | 16 XRP | Minted20:47:00+26d 1hFlagged21:46:44+6sDrained21:46:50 Flagged 6s before drain | rEM4Hr…MVD2 | NFT 000827… ↗tx 9E2EB6… ↗ |
1d ago Sep 25, 21:40:42 UTC | 16 XRP | Minted23:43:32+7d 22hFlagged21:40:40+2sDrained21:40:42 Flagged 2s before drain | rEM4Hr…MVD2 | NFT 00081F… ↗tx 0DAC60… ↗ |
1d ago Sep 25, 20:46:12 UTC | 2 XRP | Minted01:16:00+20d 20hDrained20:46:12+19h 50mFlagged16:36:36 Flagged 19h 50m after drain | rUnvhJ…UuxU | NFT 000813… ↗tx 82D86F… ↗ |
1d ago Sep 25, 20:29:12 UTC | 1 XRP | Minted23:43:32+7d 21hDrained20:29:12+1h 11mFlagged21:40:40 Flagged 1h 11m after drain | rUnvhJ…UuxU | NFT 00081F… ↗tx 89C331… ↗ |
1d ago Sep 25, 20:28:30 UTC | 1 XRP | Minted17:32:32+14d 3hDrained20:28:30+1dFlagged20:52:24 Flagged 1d after drain | rUnvhJ…UuxU | NFT 000813… ↗tx FFF3C3… ↗ |
1d ago Sep 25, 20:23:22 UTC | 1 XRP | Minted20:47:00+25d 24hDrained20:23:22+1h 23mFlagged21:46:44 Flagged 1h 23m after drain | rUnvhJ…UuxU | NFT 000827… ↗tx BEDF8B… ↗ |
2d ago Sep 24, 17:24:21 UTC | 237 XRP | Minted17:24:00+21sDrained17:24:21+3sFlagged17:24:23 Flagged 3s after drain | raDKR9…JgdK | NFT 000801… ↗tx 1AB389… ↗ |
2d ago Sep 24, 16:53:21 UTC | 67 XRP | Minted16:52:52+29sDrained16:53:21+3sFlagged16:53:23 Flagged 3s after drain | rKi3em…3bYA | NFT 000801… ↗tx CE6E19… ↗ |
Drains ≥ 10,000 XRP highlighted. Drains before the 16 Jun 2026 line predate xrp.cafe / Xaman consuming this feed and were not protected by it.
How to protect yourself (users)
- Never sign an
NFTokenCreateOffer, or any transaction, you didn't deliberately start. - Treat memos like "Verification", "Safe XRPL verify", or "idx:N;len:N" as red flags. No legitimate XRPL service uses those.
- If an NFT in your wallet shows a huge balance you never bought, do not click it (don't interact with things you do not understand). Check the URI: anything pointing to
xrpl-api.comorxrp-api.comis the drain campaign. - Burn or hide suspect NFTs from your wallet instead of interacting with them.
- Never paste a "verification" code into your terminal. If an NFT description, linked page, Discord/Twitter DM, or "support agent" tells you to open PowerShell/Terminal and paste a command, it is HijackLoader/SnappyClient or an equivalent commodity stealer. It will exfiltrate your browser cookies, saved passwords, wallet files, and stage persistence on your machine. No real XRPL service ever requires this.
- If you've been drained on-chain, the transfer cannot be reversed. If your machine was compromised (terminal-paste variant), assume cookies + saved credentials + locally stored wallet seeds are all leaked: rotate exchange/email/social passwords from a clean device, revoke any active wallet sessions, and move XRPL funds to a fresh seed generated offline on hardware you trust.
Already got the spam offers? Revoke Xaman third-party app access
If you connected your Xaman wallet to one of the phishing sites and are now being spammed with NFT offers, cancelling each offer does not stop the attack. The attacker holds an active third-party app permission on your wallet and will keep pushing offers until you revoke it.
- Open Xaman → Settings → Third-party apps.
- Look for an app you don't recognise. Most commonly the malicious entry is labelled "XPMarket", but the attacker can rename it to anything (Xaman, FuzzyBear, RLUSD, an XRPL marketplace, etc.). The displayed name is not verified.
- Tap the suspicious app.
- Scroll to the bottom and tap Revoke access.
After revoking, the attacker can no longer create offers on your behalf. If you signed anything during the session, or if you can't remember exactly what you authorized, move remaining XRP, tokens, and any LP positions to a fresh seed generated offline.
For wallet & dapp developers: automatic scam detection
Free public endpoints cover the full integration surface. No API key required; data updates every minute.
GET /api/nft/<NFTokenID>Already part of the standard NFT API. Returns the full NFT document; check the scam: true and scamType fields before rendering or accepting an offer.
curl https://api.xrpl.to/api/nft/00090000560ABF36DE406A9E7EE3B37CBBE047629EC1C40E956828E50634B54A
# → { "_id": "0009...", "scam": true, "scamType": "phishing_uri_domain", "issuer": "r3qAz...", ... }GET /api/nft/scamSingle endpoint with everything: aggregate stats, monthly timeline, top scammers/victims, recent drains, and a flat scamIssuersList (2.4K addresses today) for client-side filtering. Cache locally and filter incoming NFTs by issuer against the list; pre-empts any per-NFT round-trip for known-bad wallets. Refresh every few minutes.
curl https://api.xrpl.to/api/nft/scam
# → { "totals": { ... }, "monthlyTimeline": [ ... ], "topScammers": [ ... ],
#     "tokensDrained": [ ... ], "recentDrains": [ ... ],
# "scamIssuersList": ["r3qAz...", "rGhwR5...", ...], ... }GET /v1/scams/addresses · GET /v1/scams/check/<address>Not NFT-only. /v1/scams/addresses returns the flat union of every flagged XRPL address — the NFT-phishing issuers above plus known payment drainers — and /v1/scams/check/<address>verifies a single counterparty. Cache scamAddressesList and reject any Payment or offer to a flagged address before signing.
curl https://api.xrpl.to/v1/scams/addresses
# → { "count": ..., "sources": { "scam_accounts": ..., "nft_scam_issuers": ... },
#     "scamAddressesList": ["r...", "r...", ...], "accounts": [ ... ] }

curl https://api.xrpl.to/v1/scams/check/rNVdQM2AupHsZfGfkHKR4qfPHcLYwwbmH3
# → { "is_scam": true, "category": "...", "reason": "...", "source": "verified" }
Suggested integration: on app load, fetch /api/nft/scam once and cache the scamIssuersList. For each NFT before rendering, check nft.issuer ∈ scamIssuersList first (O(1) client-side). If the issuer is clean but you want to verify the specific NFT, follow up with GET /api/nft/<NFTokenID>and check scam in the response. Detection is already live; flags appear on-chain within seconds of a new mint or offer.
The full XRPL.to API surface (tokens, AMM pools, NFTs, traders, OHLC, holders, search, and more) is documented at xrpl.to/docs. Free, no API key required for read endpoints, no rate-limit headaches for normal use. A modern alternative to the Ripple Data API with deeper filtering and richer query parameters.